Security Ninja (Premium) — download
Download Security Ninja (Premium) free with SrmehranClub membership. Exact files as listed on the official site. No license keys or author support. GPL pre-activated.
Security Ninja (Premium) Free Download (100% Original GPL, Pre-Activated & Not Nulled Version)
Want a simple, powerful way to protect your WordPress website from hackers, malware, vulnerabilities, and brute-force attacks? Security Ninja (Premium) is one of the most advanced WordPress security plugins, trusted for its deep security scanning, firewall protection, and automated fixes—all without slowing down your site.
At Srmehranclub, you can download the 100% original, pre-activated, and not nulled or cracked version of Security Ninja Premium under a trusted GPL license, saving you up to 90% compared to the official price.
? Why Security Ninja Premium Is a Top-Tier Security Plugin
Keeping your WordPress site secure shouldn’t be complicated. Security Ninja makes it effortless.
Here’s why users love it:
-
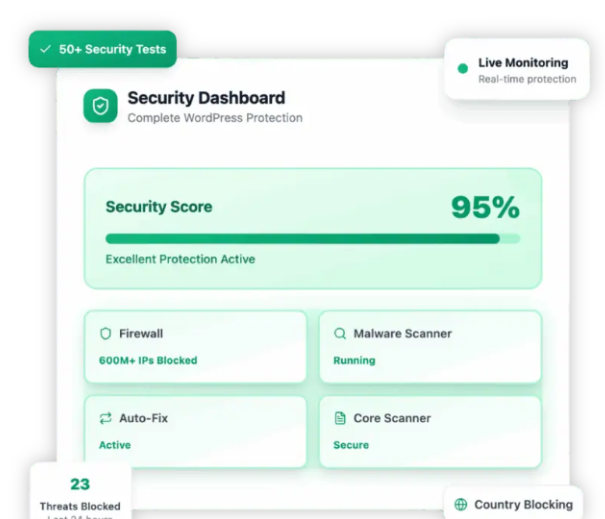
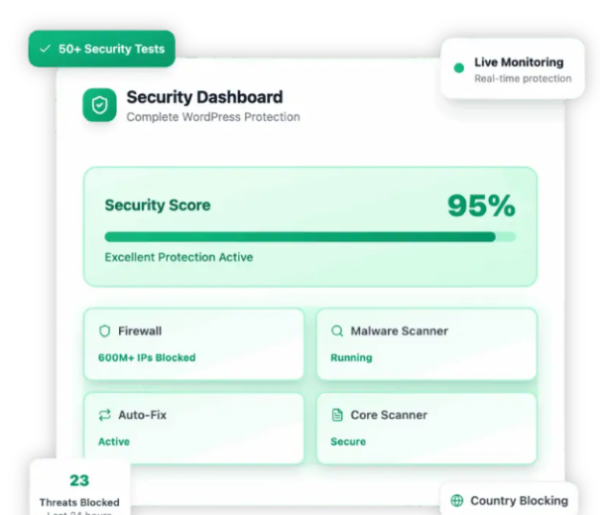
40+ detailed security tests powered by the Core Scanner
-
Malware scanner for detecting suspicious files and code
-
Real-time firewall and brute-force protection
-
Scheduled scans and automated security reporting
-
Vulnerable plugins & themes detection
-
Auto-fix options for common security issues
-
Event logging to track suspicious actions
-
IP blocking, country blocking & rate limiting
-
No core file modifications—safe and lightweight
Ever wondered how vulnerable your site really is? With Security Ninja Premium, you’ll get a full report in seconds.
?? Why Download from Srmehranclub?
Your website deserves real security—not risky nulled files.
With Srmehranclub, your Security Ninja Premium free download includes:
-
Pre-activated premium features
-
100% original GPL files
-
Never a cracked or nulled version
-
Malware-free and safe download environment
-
Free updates for active members
-
Access to the latest versions anytime
Premium protection at an unbeatable price—safe, legal, and original.
?? Who Should Use Security Ninja?
This plugin is ideal for:
-
Bloggers & content creators
-
WooCommerce store owners
-
Agencies managing multiple client sites
-
Business websites & SaaS platforms
-
Membership sites and LMS platforms
-
Anyone wanting advanced WordPress security without coding
If security matters (and it should), this plugin is a must-have.
?? Key Features of Security Ninja (Premium)
Let’s break down the powerful tools included:
-
Core Scanner with 40+ security tests
-
Malware scanning & detection
-
Firewall protection with intelligent rules
-
Brute-force login protection
-
Automatic fix suggestions for vulnerabilities
-
Scheduled scans and auto-monitoring
-
Vulnerable plugin & theme alerts
-
Event logging and activity monitoring
-
IP blocking & country-based restrictions
-
Database optimization and integrity checks
One plugin—complete WordPress protection.
?? GPL License – Safe, Legal & 100% Original
Every file at Srmehranclub is provided under the official GPL license, offering:
-
100% original, unmodified files
-
Safe, clean code (no malware or injected scripts)
-
Full editing and customization rights
-
Lifetime usage rights
-
No restrictions or hidden limitations
Premium security the right way.
?? Final Thoughts
Security Ninja Premium is one of the most comprehensive and user-friendly WordPress security plugins available. From malware detection to firewall protection and automated scans, it gives you everything needed to harden your website like a pro.
And when you download it from Srmehranclub, you get the pre-activated, not nulled, 100% original GPL version, ensuring unbeatable value with total peace of mind.
Ready to secure your website the smart way?
? FAQs (Unique)
1. Does Security Ninja Premium require coding knowledge?
Not at all—everything is beginner-friendly with one-click tools.
2. Is the version from Srmehranclub nulled?
No. We only provide 100% original GPL versions, never cracked or nulled files.
3. Can Security Ninja detect malware automatically?
Yes, the malware scanner checks for infected or suspicious files.
4. Will it slow down my website?
No. It’s lightweight and optimized to run efficiently alongside any theme or plugin.
5. Does Security Ninja include brute-force protection?
Yes, it protects against repeated login attempts and blocks abusive IPs.
Changelog
From readme.txt in the download
Version 5.305Latest1 new15 improved4 fixed1 other
New
- Agent skill – SKILL.md in the plugin folder tells Cursor and Claude-style agents how to configure Security Ninja, read scan results, and work through a harden checklist. This is separate from the WordPress Abilities API. Thank you Gabe.
Improved
- German – The bundled translation now uses Du, the same terms throughout (Schwachstelle, Core-Scanner, Malware-Scanner, Korrekturen, Anmeldung), and the strings that were still English are translated.
- Updated Freemius SDK to the latest version.
- Vulnerability Scanner – When vulnerabilities are found, the warning is the only headline. "Vulnerability Scanner" stays when the scan is clean or still running. Collapsed Details no longer leaves an empty white bar.
- Tests – Permissions-Policy example now uses current header syntax and a shorter default that leaves fullscreen, autoplay, and encrypted media alone so embedded video keeps working. Thank you Lee.
- Tests – Permissions-Policy default no longer disables payment, so Apple Pay and Google Pay checkouts keep working. Thank you Robert.
- Tests – Content-Security-Policy help and Fixes examples use a WordPress-safe enforcing policy. Script limits stay an advanced step and will not pass the test while they are Report-Only. Thank you Robert.
- Tests – MySQL permissions warns when the account has ALL PRIVILEGES on this site's database, and fails on global grants or GRANT OPTION. The help text lists the privileges WordPress, updates, and backups need. Thank you Robert.
- Tests – Security header help cleanup: removed obsolete X-Frame-Options ALLOW-FROM, fixed CSP Apache Header set syntax, and aligned X-Content-Type-Options, X-Frame-Options, HSTS, and Referrer-Policy PHP examples with the wp_headers filter.
+7 more
- Fixes – Hide WP Version now also clears the generator on RSS/Atom feeds and strips matching WordPress core ?ver= from CSS/JS asset URLs. Plugin and theme cache-busting versions are left alone.
- Firewall – Block IP Network now uses api.wpsecurityninja.com. User-agent matches stay local and are no longer sent to the shared list. Sites with the feature on download the shared list once a day.
- Firewall – Block IP Network reports are queued locally and flushed in batches (every 15 minutes or at 25 unique IPs), with a local hit count per IP.
- Firewall – Early Firewall 8G blocks are reported to the Block IP Network when WordPress imports them. User-agent matches stay local.
- Events Logger – Selected firewall and block events, including Early Firewall blocks and lost-password bans, are kept for 90 days. Other events still follow the retention you set.
- Firewall – Country block selection stays as you set it when you press Enter in another field on the Firewall settings page.
- Firewall – Request URI checks use the path only. Query parameters are checked separately, so long tokens in URLs (for example WooCommerce download links) are not mistaken for exploit paths.
Fixed
- Tests – A wp-config.php moved one level above the WordPress root now scores as a pass. A file still in the root stays a warning. Thank you Robert.
- Auto Fixer – File backups are stored as .wfbkp data files again (not .php), so the Malware Scanner no longer flags our own backups. Existing .wfbkp.php backups are migrated automatically. Thank you Tom and Masahiro.
- Scheduled Scanner – Scans started through Action Scheduler's async admin-ajax runner no longer die on a Security Ninja test nonce check (403). Internal runners skip that AJAX nonce; UI AJAX still verifies it. Thank you Kevin.
- Firewall – Repeated failed logins are reported to the Block IP Network as repeat_failed_login, which is the type the shared list accepts.
Other
Show 5 earlier versions
Version 5.3045 new21 improved5 fixed1 other
New
- Translations – Portuguese (Brazil).
- Early Firewall (Pro, beta) – Optional mode that can run the firewall before WordPress loads via PHP auto_prepend_file. Existing sites stay on WordPress hooks until you enable it. Site-local only (not Tools import/export or MainWP). Beta limitations: not available on multisite or IIS; competing security WAFs are refused (guided migration); non-WAF prepends require confirmation; disable removes Security Ninja markers only and keeps prior prepend details for manual recovery.
- Setup wizard (Pro, first run) – Optional Early Firewall step after Activate Firewall. Skip keeps the current WordPress-hooks firewall.
- Admin notice (Pro) – Dismissible heads-up on existing sites that Early Firewall is available. No automatic install.
- Events Logger (Pro) – Download the event log as CSV from the Events tab (capability + nonce + license gated, streamed in chunks for large logs). Thank you Tim.
Improved
- Translations – Full review of bundled language packs: Bulgarian, Chinese, Croatian, Danish, Dutch, Finnish, French, German, Italian, Korean, Norwegian, Portuguese (Brazil), Russian, Spanish, and Swedish.
- Events Logger – "Keep last N records" follows the number you save.
- Events Logger – Retention help text notes that selected firewall/block events can be kept longer for investigations, and that Delete all clears everything.
- Events Logger – Log rows with nested details stay readable in the events table.
- Firewall – Slimmer load path: heavy admin and cron code moved out of the always-loaded firewall class; shared 8G rules file; mail, temporary-login, and service/crawler whitelist helpers load on demand. Helps uncached PHP bootstrap cost.
- Firewall – WooCommerce checkout and payment returns are less likely to be treated as attacks. Obvious attacks are still blocked. Free and Pro.
- Firewall – SureCart checkout, product, and webhook requests are less likely to be treated as attacks, using the same approach as WooCommerce. Pro store rate limits and coupon protection apply when SureCart is active. When 2FA is on, sign in through the WordPress login. Free and Pro.
- Visitor Logging – New installs default to tracking off (existing sites keep their saved setting).
+13 more
- Firewall – Login settings page loads reliably in the free plugin.
- Firewall – Unusual cloud blocklist entries no longer interrupt the plugin admin page on PHP 8. Thank you Werner.
- Early Firewall (Pro) – Enable, Verify, and Disable update the panel without reloading the page. A spinner shows while the request runs.
- Early Firewall (Pro) – The beta notice hides once Early Firewall is installed, including while it is pending or on. Open Firewall settings jumps to the panel.
- Early Firewall (Pro) – Shorter status copy. Partial coverage is shown as On. While it is turning off, only Verify removal is shown.
- Automatic AI review – Each scheduled review runs the security tests first, then sends those results and the latest stored scans. Malware scans stay on their own schedule.
- Events Logger – User agents recorded by Early Firewall are stored cleanly, including unusual characters.
- Core Scanner and File Viewer – Path checks keep working on PHP 7.4 and older WordPress versions.
- Firewall – Existing secret access URLs stay as they are. Reset still creates a new one when you ask.
- Firewall – Visitor IP detection stays consistent across Automatic, Cloudflare, and proxy modes. If a reverse proxy sits in front of the site, add its address under Trusted proxy CIDRs.
- AI Security Advisor – Risk badges use the standard labels: low, medium, high, and critical.
- Tests – Plugin age and WordPress compatibility checks say when a plugin could not be verified, for example a premium or custom plugin, or when WordPress.org could not be reached.
- Firewall (Pro) – Firewall settings tabs and country blocking controls work with directory themes such as MyListing. Thank you Kevin.
Fixed
- Admin – Firewall sidebar no longer crushes the main settings column on laptop and tablet widths. Store toggles stay on one row with their labels.
- License_key.txt auto-activation now works when upgrading from Free to Pro. Thank you Michael.
- Tests – Quick Filter and Expand all details now sit on one row with Run Tests.
- Plugin header now includes Requires at least (WordPress 4.7) and Requires PHP (7.4), so the update screen can show both.
- Malware Scanner – Scan step timers stay in one right-hand column, and View File / Whitelist / Delete stay on one row in the findings table.
Other
Version 5.3031 new10 improved1 other
New
- Visitor IP detection – Choose how the firewall reads the visitor IP: Automatic, Cloudflare, proxy headers, or REMOTE_ADDR. Automatic trusts Cloudflare ranges by default. For another load balancer or reverse proxy, add its IPs under Trusted proxy CIDRs. Free and Pro.
Improved
- Vulnerability Scanner – Scheduled warning emails wait for a finished scan, skip plugins and themes that are gone or already patched, and do not repeat the same findings within 24 hours. Thank you Jamie.
- Deactivation – One central "Remove settings when deactivating" switch. Leave it off to keep settings, scans, logs, and cached files. Scheduled jobs still stop when the plugin is deactivated.
- Uninstall – Removing the plugin also clears module tables, settings, cached files, and related user metadata.
- Events Logger – Administrator emails now cover new accounts and role promotions.
- Events Logger – Speed improvement – When logging is off, event hooks and database writes are skipped. Broad REST API error logging stays off by default; turn it on in Events settings if you need those diagnostics.
- Settings import/export and MainWP – Events REST logging and visitor IP settings, including trusted proxy CIDRs, are included when you copy settings between sites.
- Malware Scanner – Removed the unused legacy scanner.
- MainWP – Applying settings remotely now reschedules the scanner cron when the schedule changes, and applies the same wp-config updates as the Fixes page (file editor, debug, secure cookies).
+2 more
- MainWP – Remote settings now include WooCommerce rate-limit numbers, 2FA grace period and login copy, and satellite/ASN soft-mode lists.
- Frontend – Speed improvement – Premium no longer loads unused Pro modules on public page views. Free modules are unchanged. Thank you Jose.
Other
Version 5.3026 fixed1 other
Fixed
- Firewall – Per-visitor reverse-DNS, ASN, and GeoIP caches no longer fill the WordPress options table with one row per IP. On busy sites without Redis/Memcached that could grow to hundreds of thousands of rows and cause intermittent downtime. After update, leftover rows are removed automatically in small batches. Thank you Davina.
- Firewall – Search-engine and crawler checks only run reverse-DNS when the User-Agent looks like a known crawler. Normal browser traffic no longer triggers a DNS lookup on every page view. AI crawlers (OpenAI, Perplexity, Claude) are checked against published IP ranges only.
- Firewall – Hostname-based "blocked hosts" matching (part of Filter Suspicious Queries) is off by default. URI, query string, user agent, and referrer rules still run. Developers can re-enable hostname checks with the secnin_cf_check_blocked_hosts filter.
- Firewall – Satellite/ASN softening (Pro) no longer calls the remote ASN API on every miss when the site has no object cache. With Redis or Memcached, results are cached there instead of in the database.
- Firewall – The list of remembered validated crawler IPs is limited to 200 entries so it cannot grow without bound.
- Fixes – Disable Username Enumeration now blocks anonymous REST user listing (/wp/v2/users and ?rest_route=), not only by removing the endpoint. The username enumeration security test checks that path as well. Thank you Elias.
Other
Version 5.3011 improved1 fixed1 other
Improved
- Vulnerability Scanner – Update notices now say we are tracking more known vulnerabilities in the database, not that vulnerabilities were "downloaded" to the site. Thank you Tom.
Fixed
- Fixes – Saving Security Fixes with "Disable debug mode" off no longer forces WP_DEBUG to true in wp-config.php. Thank you Mike.
Other
Version 5.3001 improved2 fixed1 other
Improved
- Firewall – Filter Suspicious Queries help text now states that it includes reverse-DNS hostname checks, separate from Cloud Firewall and Prevent Banned IPs.
Fixed
- Firewall – Removed the blocked_kanagawa hostname rule again (Japanese prefecture / OCN false positives). Thank you Masahiro.
- Scheduled Scanner – Security Testing emails no longer fire on message-only diffs or HTTP timeout Warning/Good flaps.
Other
Showing the latest 6 of 16 versions.



Reviews
There are no reviews yet.